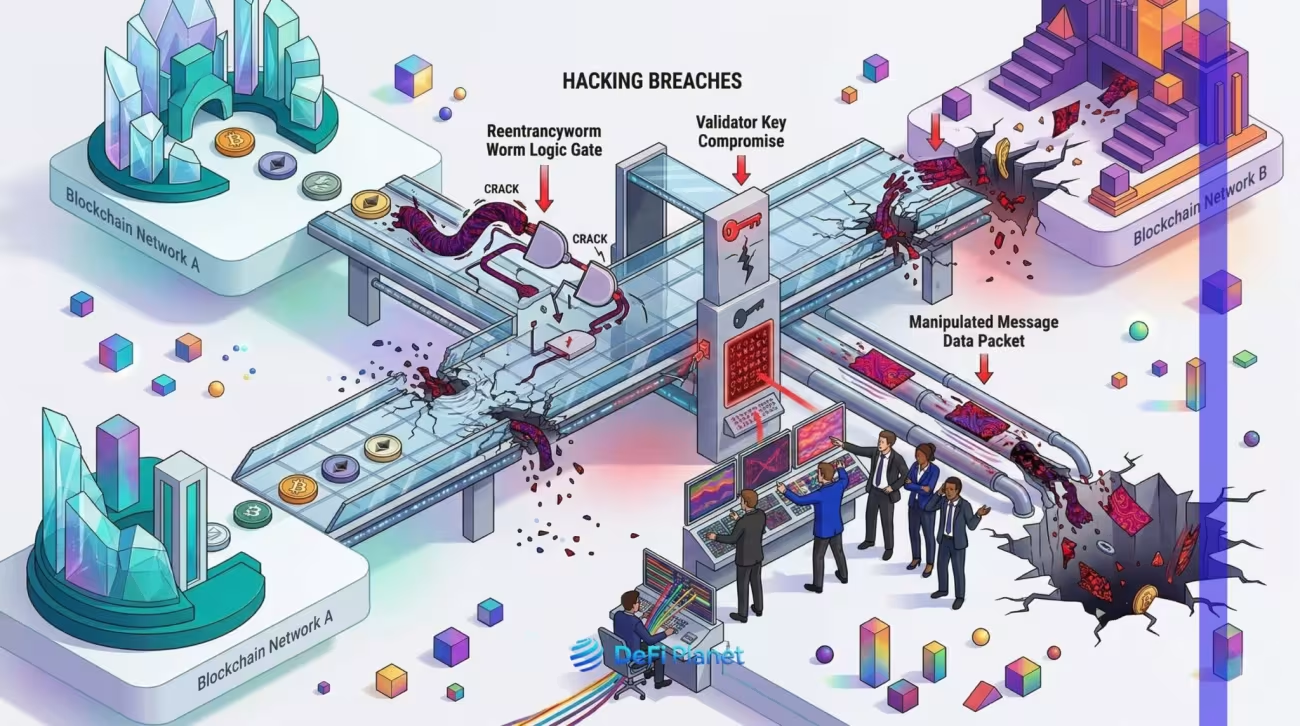
The rapid expansion of decentralized finance has created a financial ecosystem in which digital assets can move between multiple blockchain networks. However, the infrastructure connecting these networks has also become one of the most vulnerable components of the cryptocurrency industry. Cross-chain bridges, designed to facilitate interoperability between independent blockchains, have repeatedly become targets for sophisticated cyberattacks, resulting in billions of dollars in losses.
In August 2022, blockchain analytics company Chainalysis estimated that approximately $2 billion in cryptocurrency had been stolen across 13 cross-chain bridge attacks. These incidents represented 69% of all cryptocurrency funds stolen during the first seven months of that year.
The situation became even more concerning when Chainalysis published its full-year 2022 findings in February 2023. The company reported that decentralized finance protocols accounted for $3.1 billion, or 82.1%, of all cryptocurrency stolen by hackers during 2022. Of that amount, 64% came from cross-chain bridge protocols.
The figures revealed a fundamental problem in decentralized finance: while individual blockchains can maintain sophisticated consensus and transaction-verification mechanisms, the systems connecting them introduce additional layers of trust, software and infrastructure that can become attractive targets for attackers.
Major incidents involving Ronin Network, Wormhole, Harmony Horizon Bridge and Nomad exposed different weaknesses in this infrastructure. Some attackers compromised validator private keys, others exploited smart-contract verification errors, and one attack demonstrated how a flawed initialization process could allow fraudulent transactions to be accepted on a massive scale.
These incidents were not isolated programming mistakes. Together, they exposed structural weaknesses involving custody, transaction authorization, cryptographic verification, operational security and the concentration of valuable assets within bridge contracts.
The consequences extend beyond individual cryptocurrency projects. Because multiple decentralized applications depend on cross-chain infrastructure, a successful attack can affect liquidity providers, token holders, lending platforms, decentralized exchanges and other interconnected financial services.
The $2 Billion Warning: How Cross-Chain Bridges Became a Major Hacking Target
On August 2, 2022, Chainalysis published an investigation titled Vulnerabilities in Cross-chain Bridge Protocols Emerge as Top Security Risk.
The report followed the exploitation of Nomad Bridge and estimated that approximately $2 billion had been stolen across 13 cross-chain bridge attacks. Most of the losses had occurred during 2022.
Chainalysis estimated that bridge attacks represented 69% of all cryptocurrency funds stolen during the first seven months of the year.
The report also highlighted the involvement of North Korean-linked hackers, estimating that approximately $1 billion had been stolen by these actors from bridges and other DeFi protocols during the same period.
These findings highlighted a shift in the cryptocurrency threat landscape. Rather than concentrating exclusively on centralized exchanges and individual user wallets, attackers were increasingly targeting the infrastructure that supported the movement of assets across blockchain networks.
The Full-Year 2022 Figures Were Even More Significant
Chainalysis subsequently reported that 2022 was the largest year on record for cryptocurrency hacking at the time, with approximately $3.8 billion stolen from cryptocurrency businesses.
Decentralized finance protocols accounted for $3.1 billion of those losses, representing 82.1% of all cryptocurrency stolen by hackers.
Cross-chain bridge protocols accounted for 64% of the amount stolen from DeFi platforms.
The findings demonstrated that bridges had become an especially attractive target because they often concentrated large quantities of cryptocurrency in smart contracts or custodial infrastructure.
For attackers, compromising one critical bridge component could potentially provide access to hundreds of millions of dollars in digital assets.
What Is a Cross-Chain Blockchain Bridge?
A blockchain bridge is a protocol that enables digital assets or information to move between two or more independent blockchain networks.
Blockchain networks generally maintain separate transaction histories, consensus mechanisms and execution environments.
For example, Ethereum and Solana operate using different technical architectures. An asset existing on Ethereum cannot simply be transferred to Solana as though both networks shared one transaction database.
A bridge provides an intermediary mechanism that allows the networks to communicate and coordinate transactions.
Depending on its architecture, a bridge may transfer representations of digital assets, facilitate token swaps, relay messages or enable smart contracts on one blockchain to respond to events occurring on another.
How Lock-and-Mint Bridges Work
One of the most common bridge designs uses a lock-and-mint mechanism.
When a user wants to transfer an asset from one blockchain to another, the original token is locked in a smart contract on the source blockchain.
The bridge then verifies the deposit and authorizes the creation of an equivalent wrapped token on the destination blockchain.
For example, a user transferring ETH from Ethereum to Solana through Wormhole may deposit ETH into the bridge contract on Ethereum and receive Wormhole-wrapped ETH on Solana.
The wrapped asset represents a claim backed by the original ETH held by the bridge.
The process generally involves the following steps:
- Asset deposit: The user sends the original cryptocurrency to the bridge contract on the source blockchain.
- Transaction detection: The bridge's verification infrastructure observes the deposit event.
- Authentication: Validators, cryptographic proofs or another verification mechanism establish that the event is legitimate.
- Cross-chain messaging: The authenticated transaction information is delivered to the destination blockchain.
- Token issuance: The destination contract releases or mints the corresponding asset.
- Reverse transfer: When the user returns to the original network, the wrapped asset is burned or otherwise accounted for before the original asset is released.
The most critical part of this process is authentication.
The destination blockchain must establish that the source-chain transaction actually occurred and that the message authorizing the corresponding action is valid.
If an attacker can forge that authorization, the bridge may issue tokens without receiving the required collateral or release assets without a legitimate withdrawal request.
Liquidity-Based Bridges
Not every bridge uses a direct lock-and-mint architecture.
Some protocols maintain liquidity pools on multiple blockchains.
Users deposit one asset into a liquidity pool on the source network and receive an equivalent asset from a pool on the destination network.
These arrangements can offer faster transfers and reduce certain operational complications associated with wrapped assets.
However, they introduce other risks involving liquidity availability, pool accounting, pricing mechanisms and smart-contract authorization.
Regardless of the architecture, every bridge must establish a reliable method for verifying that cross-chain transactions are legitimate.
Why Blockchain Bridges Are So Vulnerable
Blockchain bridges have several characteristics that make them attractive targets for sophisticated attackers.
1. Concentrated Cryptocurrency Reserves
Many bridges hold substantial amounts of cryptocurrency in relatively small numbers of smart contracts or custodial accounts.
These assets provide backing for tokens issued on destination blockchains.
Consequently, a successful attack against the bridge's custody or authorization mechanisms can expose an enormous quantity of cryptocurrency.
Chainalysis identified this concentration of funds as one of the principal reasons bridges became attractive targets.
2. Multiple Security Boundaries
A bridge must operate across independent blockchain environments, each with its own technical requirements.
This creates a larger attack surface than many conventional decentralized applications.
Security depends not only on smart contracts but also on validator infrastructure, communication systems, signing keys, administrative privileges and off-chain services.
Research published by security researchers from Quantstamp and Zircuit in 2023 examined bridge attacks and emphasized that many incidents involved weaknesses in off-chain information technology practices rather than vulnerabilities in on-chain code alone.
3. Dependence on External Verification
Some bridges rely on external validators or oracle networks to confirm transactions occurring on another blockchain.
If these systems are compromised or incorrectly configured, they may authorize fraudulent cross-chain messages.
The destination blockchain may then execute an operation that would never have been accepted under the source blockchain's normal transaction rules.
4. Complex Smart-Contract Logic
Bridge contracts frequently handle deposits, withdrawals, token minting, burning, message verification and administrative upgrades.
Small programming mistakes can create opportunities for attackers to bypass authorization checks or manipulate contract state.
The more complex the architecture, the more difficult it becomes to identify every possible failure scenario.
5. Operational Security Failures
Not every bridge attack involves a programming vulnerability.
Private keys may be stolen through phishing, social engineering, malware or compromised infrastructure.
Even a technically sound multisignature system can fail if attackers gain access to enough signing keys.
The Ronin and Harmony incidents demonstrated the importance of operational security and independent key management.
The Ronin Network Hack: Approximately $625 Million Stolen Through Compromised Validator Keys
One of the largest cryptocurrency bridge attacks occurred against Ronin Network, an Ethereum-linked sidechain developed to support Axie Infinity.
Axie Infinity became one of the most prominent blockchain gaming projects during the 2021 cryptocurrency boom.
The game used Ronin to reduce transaction costs and improve the user experience compared with conducting every transaction directly on Ethereum.
To move assets between Ethereum and Ronin, users relied on the Ronin Bridge.
On March 23, 2022, attackers gained sufficient control over the bridge's validator signing infrastructure to authorize fraudulent withdrawals.
The stolen assets included 173,600 ETH and 25.5 million USDC, worth approximately $625 million at the time.
How the Ronin Validator System Worked
Ronin used nine validator nodes to authorize bridge transactions.
Five validator signatures were required to approve a withdrawal.
This arrangement was intended to prevent one compromised validator from independently controlling the bridge's funds.
However, the security of the system depended on keeping at least five signing keys outside an attacker's control.
Once attackers obtained sufficient private keys, the multisignature protection could no longer prevent fraudulent withdrawals.
How the Attackers Compromised the Validators
Investigations revealed that the attack involved social engineering and the compromise of Sky Mavis infrastructure.
The attackers used a fraudulent employment opportunity to target an employee of the company.
After gaining access to the corporate environment, they obtained control of validator signing capabilities.
The attackers also exploited an earlier operational arrangement involving the Axie DAO validator.
During a period of heavy transaction volume, Sky Mavis had received authorization to sign transactions on behalf of the Axie DAO validator.
That authorization was not properly revoked after the operational arrangement was no longer required.
This meant that compromising the Sky Mavis infrastructure provided access to enough validator authority to meet the withdrawal threshold.
Why the Theft Went Undetected for Six Days
The fraudulent transactions occurred on March 23, but the breach was not discovered until March 29.
The incident came to light after a user attempted to withdraw 5,000 ETH and encountered difficulties completing the transaction.
The six-day delay exposed serious weaknesses in the bridge's monitoring and incident-detection procedures.
A bridge holding hundreds of millions of dollars should have systems capable of identifying unusual withdrawal activity and suspicious validator signatures.
FBI Attribution and Recovery Efforts
In April 2022, the FBI attributed the Ronin theft to Lazarus Group, a North Korean state-linked cyber actor.
The US Treasury Department subsequently sanctioned cryptocurrency addresses associated with the operation.
In September 2022, US authorities announced the recovery of approximately $30 million in cryptocurrency associated with the Ronin theft, demonstrating that blockchain tracing and cooperation with cryptocurrency businesses can support asset recovery.
Sky Mavis later reopened the Ronin Bridge following security improvements and arrangements to restore affected user balances.
The incident became a major warning about the risks of validator concentration, compromised corporate infrastructure and insufficient monitoring.
The Wormhole Hack: $320 Million Stolen Through a Verification Vulnerability
On February 2, 2022, Wormhole suffered another major bridge exploit involving approximately $320 million in cryptocurrency.
Wormhole is a cross-chain messaging protocol designed to connect multiple blockchain networks, including Ethereum and Solana.
The attack allowed an unauthorized party to create approximately 120,000 Wormhole-wrapped ETH on Solana without depositing the corresponding amount of ETH into the bridge.
How Wormhole's Guardian System Worked
Wormhole used a network of Guardians to observe events on supported blockchains and produce cryptographically authenticated messages.
These messages, known as Verified Action Approvals, enabled applications on destination networks to verify that particular events had occurred on source networks.
For example, when a user transferred ETH through the bridge, the Guardian network would observe the relevant transaction and generate an authenticated message authorizing the corresponding destination-chain operation.
The system therefore depended on the integrity of the Guardian signatures and the smart contracts responsible for verifying them.
How the Attacker Bypassed Verification
The vulnerability involved the Solana implementation of Wormhole's signature-verification process.
The attacker exploited an incorrect account-validation mechanism associated with a Solana system-program account.
By supplying a forged verification context, the attacker was able to bypass the intended signature validation and create a fraudulent message.
The bridge accepted the message as legitimate and issued approximately 120,000 wrapped ETH on Solana.
The attacker subsequently transferred a substantial portion of those tokens to Ethereum and exchanged them for real ETH held by the bridge.
The resulting loss was approximately $320 million at the time of the incident.
Jump Crypto Replenished the Missing ETH
Wormhole suspended bridge operations after discovering the vulnerability and subsequently deployed a patch.
Jump Crypto, which supported the Wormhole ecosystem, replenished the missing ETH to restore the backing of the wrapped assets.
This intervention helped prevent the incident from leaving users with substantially undercollateralized wrapped ETH.
However, the attack demonstrated that even a bridge supported by a large development organization could suffer a critical failure in its cross-chain verification logic.
The Harmony Horizon Bridge Hack: $100 Million Lost Through Multisignature Compromise
On June 23, 2022, Harmony announced that its Horizon Bridge had been compromised, resulting in the theft of approximately $100 million in digital assets.
Horizon was designed to connect Harmony with Ethereum and other blockchain environments.
The incident involved the compromise of the private keys controlling the bridge's multisignature wallet.
How the Multisignature System Was Compromised
The Horizon Bridge used a multisignature arrangement that required two of five private keys to authorize transactions.
Attackers gained control of two keys, allowing them to satisfy the authorization requirement and withdraw assets.
This revealed a significant weakness in the bridge's security architecture.
Although multisignature technology is intended to reduce dependence on a single key, the arrangement provided insufficient protection against a compromise involving two signing credentials.
The problem was not simply the existence of multiple keys. It was the degree of independence between the systems and individuals responsible for protecting them.
North Korean Attribution
In January 2023, the FBI confirmed that Lazarus Group and APT38 were responsible for the Harmony Horizon Bridge theft.
The stolen cryptocurrency was subsequently moved through multiple transactions and laundering services.
In May 2023, Elliptic reported that approximately $1.4 million in cryptocurrency associated with the stolen funds had been frozen through cooperation with Binance and Huobi.
The case demonstrated that even when stolen assets move across multiple blockchains, public transaction records can help investigators trace their movement.
The Nomad Bridge Hack: How a Single Initialization Error Enabled a Mass Exploit
On August 1, 2022, Nomad Bridge experienced one of the most unusual cross-chain exploits in cryptocurrency history.
Approximately $190 million in digital assets was drained from the bridge.
Unlike Ronin and Harmony, which involved compromised signing keys, the Nomad incident resulted from a smart-contract verification failure.
The Root Cause: An Incorrect Trusted Root
Nomad used a messaging system that relied on committed roots to establish whether cross-chain messages were valid.
During a contract upgrade, an initialization error introduced an incorrect default value for the trusted root.
The contract effectively treated a zero-value root as an acceptable confirmation value.
This meant that messages could pass a critical validation check without satisfying the intended cryptographic verification requirements.
As a result, attackers could submit fraudulent messages that the bridge accepted as legitimate.
Why the Attack Spread to Hundreds of Wallets
The first attacker demonstrated that the bridge could be drained by submitting a fraudulent withdrawal message.
Once the transaction became visible on the public blockchain, other participants began copying the exploit.
They modified the recipient addresses and transaction details while repeating the same basic vulnerability.
This created a mass-exploitation event involving numerous wallets.
Unlike attacks that depend on a single organized criminal group, the Nomad incident attracted opportunistic participants who could replicate the transaction pattern after observing the initial exploit.
Some participants claimed to be security researchers or white-hat hackers, but taking funds without authorization does not automatically become legitimate security research.
How Much Was Recovered?
Nomad requested that users and security researchers return the stolen assets.
The project established a recovery wallet and discussed incentives for returning cryptocurrency.
Reports in the days following the attack documented the return of a portion of the stolen assets.
However, recovery remained incomplete, illustrating the difficulty of restoring funds after a large-scale decentralized exploit.
The Nomad incident demonstrated that a single contract configuration error can have consequences comparable to a sophisticated private-key compromise.
Four Different Attacks, One Fundamental Problem
The Ronin, Wormhole, Harmony and Nomad incidents involved different technical mechanisms, but they exposed a common weakness: the failure of the systems responsible for authorizing cross-chain transactions.
| Bridge | Attack date | Approximate loss | Main vulnerability |
|---|---|---|---|
| Wormhole | February 2022 | $320 million | Signature verification bypass |
| Ronin | March 2022 | $625 million | Five compromised validator keys |
| Harmony Horizon | June 2022 | $100 million | Two compromised multisig keys |
| Nomad | August 2022 | $190 million | Smart-contract initialization error |
Combined, these four incidents resulted in more than $1.2 billion in estimated losses.
Their significance lies not only in the financial damage but also in the different layers of bridge infrastructure that failed.
Ronin exposed weaknesses in key custody and corporate security. Wormhole exposed a cryptographic verification problem. Harmony demonstrated that a low-threshold multisignature system could become a single point of failure. Nomad showed how an incorrect contract initialization could undermine the entire message-authentication process.
These examples make clear that bridge security cannot be evaluated through smart-contract audits alone.
Why Multisignature Wallets Do Not Automatically Make Bridges Secure
Multisignature wallets require multiple private keys to approve transactions.
For example, a five-of-nine arrangement requires at least five independent signatures before a withdrawal can be executed.
This reduces the risk associated with a single compromised key.
However, the system remains vulnerable if attackers can compromise enough keys to satisfy the required threshold.
The Ronin attack demonstrated this problem with five compromised keys out of nine.
The Harmony attack showed another weakness involving two compromised keys out of five.
These incidents illustrate that the number of signatures is only one part of the security equation.
Organizations must also consider:
- Whether keys are stored on independent infrastructure.
- Whether validators are operated by genuinely independent organizations.
- Whether access credentials are protected by hardware security modules.
- Whether employees have excessive administrative privileges.
- Whether emergency key revocation is possible.
- Whether transaction approvals are monitored in real time.
- Whether a compromised validator can be detected before the withdrawal threshold is reached.
A bridge with nine validators may still be effectively centralized if most signing authority is controlled by one organization.
The Role of North Korean Hackers in DeFi Attacks
North Korean-linked cyber operations became a major concern for the cryptocurrency industry during 2022.
Chainalysis estimated that North Korean-linked hackers stole approximately $1.7 billion in cryptocurrency during the year across several operations.
Approximately $1.1 billion of that amount came from attacks against decentralized finance protocols.
The Ronin and Harmony bridge incidents were particularly significant because investigators attributed both operations to Lazarus Group or associated North Korean-linked actors.
These attacks highlighted the possibility that cryptocurrency theft could be used as a source of revenue for state-linked cyber operations.
Why Cryptocurrency Bridges Are Attractive to State-Linked Actors
Large bridges can hold substantial reserves of cryptocurrency while relying on complex technical systems that require specialized knowledge to secure.
Attackers with sufficient resources can conduct prolonged reconnaissance, compromise employees, study publicly available smart-contract code and search for weaknesses in signing infrastructure.
Successful attacks can produce large quantities of cryptocurrency in a relatively short period.
However, moving stolen cryptocurrency does not necessarily make it anonymous.
Most public blockchains maintain permanent transaction records that can be analyzed by specialized investigators.
Attackers therefore often attempt to complicate tracing through multiple transactions, token conversions, cross-chain transfers and privacy-enhancing services.
How Stolen Cryptocurrency Is Laundered
Chainalysis documented how North Korean-linked actors moved stolen funds through decentralized exchanges, mixers and other cryptocurrency services.
In some cases, stolen assets were converted into more liquid cryptocurrencies before being transferred to additional services.
Following the August 2022 sanctions against Tornado Cash, Chainalysis observed changes in the services used by North Korean-linked hackers.
The company's February 2023 analysis also identified the use of Sinbad, a custodial Bitcoin mixer, in laundering activity associated with North Korean-linked thefts.
These findings demonstrate that the cryptocurrency laundering ecosystem can adapt when law enforcement and regulators disrupt particular services.
Why Blockchain Transparency Can Help Recover Stolen Funds
Despite the sophistication of cryptocurrency theft operations, public blockchains provide an important investigative advantage.
Transactions are permanently recorded, allowing investigators to trace the movement of stolen assets between wallet addresses.
Blockchain analytics companies can examine transaction patterns, identify relationships between wallets and follow funds across multiple networks.
When stolen assets reach centralized exchanges or custodial services, investigators may cooperate with those providers to freeze funds where legally and technically possible.
The recovery of approximately $30 million associated with the Ronin theft demonstrated that blockchain transparency can support law-enforcement efforts.
However, recovery is not guaranteed.
Assets may be transferred through services that do not cooperate with investigators, converted into other cryptocurrencies or moved through complex transaction paths.
The speed of incident detection is therefore critical.
The sooner suspicious transactions are identified, the greater the opportunity to trace and potentially restrict the movement of stolen assets.
How Bridge Attacks Create Systemic Risks for Decentralized Finance
The consequences of a bridge exploit can extend well beyond the protocol directly attacked.
DeFi applications frequently depend on wrapped tokens and cross-chain liquidity to operate across multiple networks.
If a bridge creates tokens without adequate collateral, the value of those tokens may no longer be fully backed by the original assets.
This can create problems for lending protocols, decentralized exchanges and liquidity pools that accept the wrapped tokens as collateral or trading assets.
Undercollateralized Wrapped Tokens
In a conventional lock-and-mint system, the amount of wrapped assets issued should correspond to the assets held by the bridge.
If attackers mint tokens without depositing the required collateral, the backing relationship breaks down.
Holders may believe that each wrapped token represents a redeemable claim on an original asset, even though the underlying reserves are insufficient.
This can lead to sudden losses when users attempt to redeem their tokens.
Liquidity Pool Contagion
DeFi applications often use wrapped assets in lending markets and liquidity pools.
If a compromised bridge asset loses its backing, protocols holding that asset may suffer collateral shortfalls.
Users can face unexpected liquidation, reduced liquidity and difficulties withdrawing funds.
These effects can spread across interconnected applications even when those applications were not directly exploited.
Confidence and Market Risk
Large bridge attacks can undermine confidence in the reliability of cross-chain assets.
Investors may withdraw liquidity, reduce exposure to affected tokens or avoid using particular bridge protocols.
This can increase market volatility and weaken the liquidity of decentralized financial applications.
Bridge security is therefore not merely a technical issue. It is also a question of financial risk management and ecosystem stability.
Why Auditing Alone Cannot Guarantee Bridge Security
Smart-contract audits are important, but they cannot guarantee that a bridge is secure.
An audit examines code and attempts to identify weaknesses in its implementation.
However, bridge attacks can originate from compromised private keys, malicious employees, insecure cloud infrastructure, incorrect validator configurations or failures in operational procedures.
Even a well-audited contract can become vulnerable when an attacker compromises the infrastructure responsible for authorizing transactions.
For this reason, bridge security requires a broader approach that combines software assurance, cryptographic verification, operational security and continuous monitoring.
How the Industry Can Strengthen Cross-Chain Bridge Security
The major attacks of 2022 demonstrated that securing bridge infrastructure requires multiple independent defensive layers.
1. Improve Private-Key Management
Validator private keys should be stored using secure hardware-backed systems, including hardware security modules and appropriately configured signing environments.
Key access should be restricted through role-based permissions, strong authentication and independent operational controls.
Organizations should also implement key rotation, secure backup procedures and emergency revocation mechanisms.
Where possible, signing authority should be distributed among genuinely independent operators rather than concentrated within one company.
2. Use Stronger Cross-Chain Verification
Bridge systems should minimize dependence on external statements that cannot be independently verified.
Cryptographic proofs, light clients and other verifiable mechanisms can help establish whether a source-chain event actually occurred.
The destination network should verify the authenticity of the message before executing an operation.
Different verification architectures involve different assumptions, so developers must carefully evaluate their security trade-offs.
3. Introduce Transaction Limits and Rate Controls
High-value bridges should implement withdrawal limits and transaction rate controls.
These measures can restrict how quickly funds can leave the system if an attacker successfully compromises part of the infrastructure.
For example, unusually large withdrawals could require additional verification or a temporary delay before execution.
Rate limits do not eliminate the underlying vulnerability, but they can reduce the amount of damage an attacker can cause during the initial stages of an exploit.
4. Implement Emergency Circuit Breakers
Bridge protocols should be able to temporarily pause suspicious operations when abnormal behavior is detected.
Automated circuit breakers can help prevent a compromised bridge from continuing to issue tokens or release collateral.
However, emergency controls must themselves be carefully designed to avoid creating a single administrative point of failure.
5. Conduct Continuous Security Testing
Independent audits should be combined with fuzz testing, formal verification, static analysis and adversarial testing.
Security assessments should cover both on-chain contracts and off-chain infrastructure.
Developers should also reassess security whenever contracts are upgraded, validators are changed or new blockchain networks are integrated.
6. Monitor Transactions Across Multiple Chains
Bridge operators should continuously monitor both source and destination networks.
Monitoring should identify suspicious withdrawals, unexpected token issuance, unusual validator signatures and discrepancies between locked collateral and issued assets.
Real-time cross-chain monitoring can help detect attacks before an attacker has time to drain substantial reserves.
7. Establish Responsible Bug Bounty Programs
Independent security researchers can help identify vulnerabilities before malicious actors exploit them.
Bridge operators should provide clear vulnerability disclosure procedures and meaningful rewards for critical findings.
Programs should also establish secure communication channels and defined timelines for handling reports.
8. Improve Incident Response and Recovery Procedures
Every bridge should have an incident-response plan covering transaction suspension, key revocation, forensic investigation and public communication.
Operators should know who can authorize an emergency shutdown and how user assets will be protected during an investigation.
Transparent communication is essential for limiting uncertainty and helping users understand the risks associated with an incident.
Newer Approaches to Cross-Chain Security
The bridge attacks of 2022 accelerated research into alternative approaches to interoperability.
Several technologies aim to reduce the need for users to trust a small group of validators or centralized operators.
Light-Client Verification
Light clients allow one blockchain to verify information about another blockchain's state without independently running a complete node for the source network.
Depending on the design, a destination chain can verify cryptographic evidence associated with source-chain consensus.
This can reduce reliance on external committees that simply attest that a transaction occurred.
However, light-client systems still require careful implementation and must account for differences in consensus mechanisms, finality and network upgrades.
Zero-Knowledge Proofs
Zero-knowledge proofs can be used to demonstrate that a particular computation or statement is valid without revealing all the underlying information.
In cross-chain systems, cryptographic proofs can help verify source-chain state or transaction conditions.
These techniques can reduce certain trust assumptions, although they introduce their own implementation, cryptographic and computational challenges.
Decentralized Oracle Networks
Decentralized oracle networks distribute responsibility for observing and transmitting information between blockchains.
Rather than depending on one operator, multiple independent nodes can participate in validating cross-chain messages.
However, decentralization must be genuine. The security of an oracle network depends on operator independence, key protection, consensus thresholds and the quality of its monitoring mechanisms.
Defense-in-Depth Architecture
Modern cross-chain systems increasingly emphasize multiple independent security layers.
These can include decentralized verification networks, independent risk-monitoring systems, transaction limits, secure key custody and emergency shutdown mechanisms.
The objective is to ensure that compromising one component does not automatically provide access to all bridge funds.
What the Bridge Attacks Mean for the Future of DeFi
Cross-chain interoperability remains essential to the development of blockchain technology.
As new networks and layer-2 systems emerge, users increasingly expect digital assets and applications to operate across different ecosystems.
However, the attacks of 2022 demonstrated that connecting blockchains creates additional security responsibilities that cannot be ignored.
The industry must move beyond the assumption that a bridge is secure simply because the underlying blockchains have strong consensus mechanisms.
Bridge operators must demonstrate that their own verification, custody and communication infrastructure can withstand sophisticated attacks.
Investors and users also need to evaluate the specific security assumptions of each bridge rather than treating all cross-chain services as equivalent.
The most important developments will likely involve stronger cryptographic verification, independent validator infrastructure, improved key management and continuous transaction monitoring.
Research into cross-chain security is also becoming more sophisticated. A 2023 study by researchers associated with Quantstamp and Zircuit examined bridge attacks from 2022 and 2023, identifying weaknesses involving custodians, communicators and debt-issuance mechanisms.
Its findings reinforced the importance of examining the entire bridge architecture rather than focusing exclusively on smart-contract code.
Conclusion: Blockchain Bridges Must Be as Secure as the Assets They Connect
The theft of billions of dollars through cross-chain bridge attacks exposed one of the most serious weaknesses in decentralized finance.
Bridges provide essential infrastructure for connecting independent blockchain networks, but their operation introduces additional layers of trust involving smart contracts, validators, cryptographic proofs, private keys and off-chain communication systems.
The Ronin attack demonstrated how compromised validator keys could authorize fraudulent withdrawals worth approximately $625 million. Wormhole exposed a vulnerability in cross-chain signature verification that enabled unauthorized token creation. Harmony highlighted the dangers of compromised multisignature credentials, while Nomad showed how an incorrect contract initialization could undermine an entire message-validation system.
These incidents also revealed that decentralization does not automatically guarantee security. A blockchain may have a large and distributed validator network while its bridge depends on a small group of signing authorities or external verification services.
The broader lesson is that interoperability must be built on verifiable security rather than assumptions of trust.
Developers need stronger cryptographic verification, independent infrastructure, secure private-key management, transaction limits and continuous monitoring. Users and investors must also understand that a bridge introduces risks that are separate from those of the blockchains it connects.
Cross-chain technology has the potential to create a more connected financial ecosystem. However, its long-term success will depend on whether the industry can protect the infrastructure responsible for moving billions of dollars between independent networks.
Without stronger security architecture and operational discipline, blockchain bridges will remain attractive targets for sophisticated attackers and a persistent source of systemic risk for decentralized finance.
```
- Log in to post comments